Cybersecurity Project · Network Security
Secure Enterprise Network Design
Three Cisco enterprise-network architecture case studies covering multi-site connectivity, secure data-center design, segmentation, firewall controls, and VPN architecture.
Academic / technical network-design projectContext & Scope
This project contains three related enterprise-network design case studies created in Cisco Packet Tracer. It demonstrates academic and technical network-security design experience and is not presented as professional Cisco network-engineering employment.
Objective
Design enterprise network architectures that combine availability, segmentation, routing, secure management, access control, perimeter security, and secure site-to-site connectivity.
Design Approach
- Designed and documented three related enterprise-network case studies in Cisco Packet Tracer.
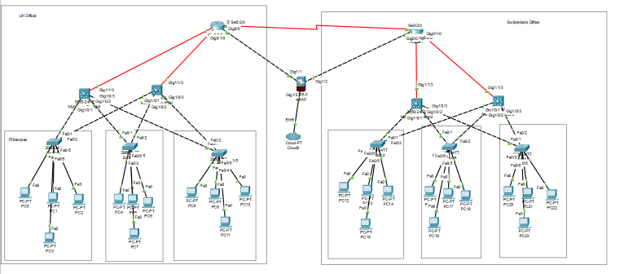
- Developed a UK–Switzerland multi-site architecture using segmentation, routing, secure management, and inter-site connectivity.
- Developed a secure data-center redesign incorporating VLAN segmentation, Layer 3 switching, ACLs, firewall controls, NAT/PAT, and DMZ concepts.
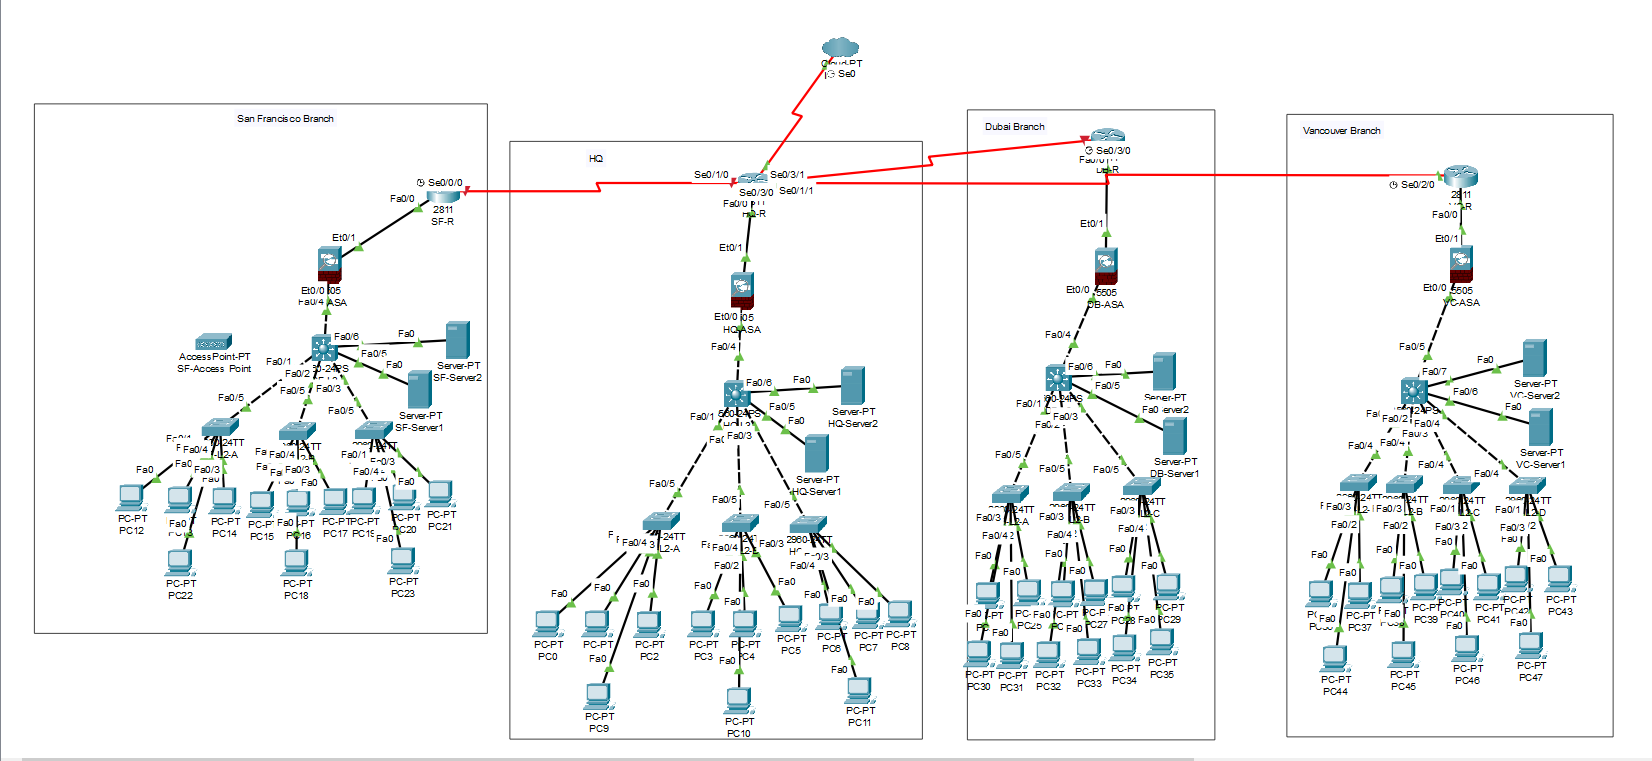
- Developed a global HQ-to-branch architecture spanning San Francisco, Dubai, and Vancouver with routed connectivity and site-to-site IPsec VPN design.
- Reviewed original configurations and topology decisions to identify security and design improvement opportunities.
Technical Implementation
- Created original Packet Tracer network topologies for multiple enterprise scenarios.
- Implemented VLAN segmentation and IPv4 subnetting to separate network functions and traffic.
- Configured Layer 3 switching, static routing, and OSPF across the design scenarios.
- Used ACLs and Cisco ASA concepts to control and restrict network access.
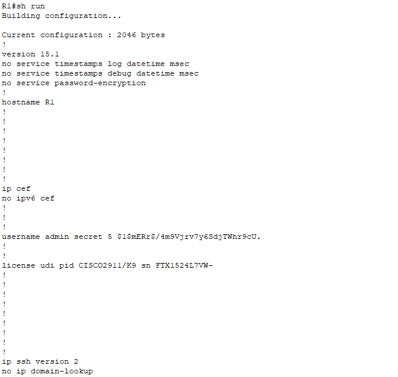
- Implemented secure-management concepts including SSH configuration.
- Documented DMZ, NAT/PAT, and site-to-site IPsec VPN configurations and supporting technical evidence.
Technical Evidence
Selected original Packet Tracer and configuration evidence from the three network-design case studies.
Experience Boundary
These architectures were designed and documented in Cisco Packet Tracer as technical case studies. They demonstrate network-design and security concepts but do not represent production networks that I professionally operated for the organisations represented in the scenarios.
Security Relevance
The project demonstrates network segmentation, routing and switching, firewall-oriented access control, secure administrative access, DMZ concepts, VPN architecture, IP addressing, and the security implications of enterprise network-design decisions.