Cybersecurity Project · Malware Analysis
Ransomware Analysis — LockBit & BlackCat (ALPHV)
Comparative static and dynamic malware analysis of two ransomware families inside an isolated Windows laboratory environment.
Academic / technical projectContext & Scope
This project investigated LockBit and BlackCat (ALPHV) ransomware in an isolated Windows lab. The work was performed as controlled cybersecurity project activity and is not presented as professional ransomware incident-response experience.
Objective
Examine and compare observable ransomware behaviour using static and dynamic analysis techniques, document technical evidence, and identify indicators relevant to malware investigation and incident response.
Approach
- Prepared and used an isolated Windows laboratory environment for controlled malware investigation.
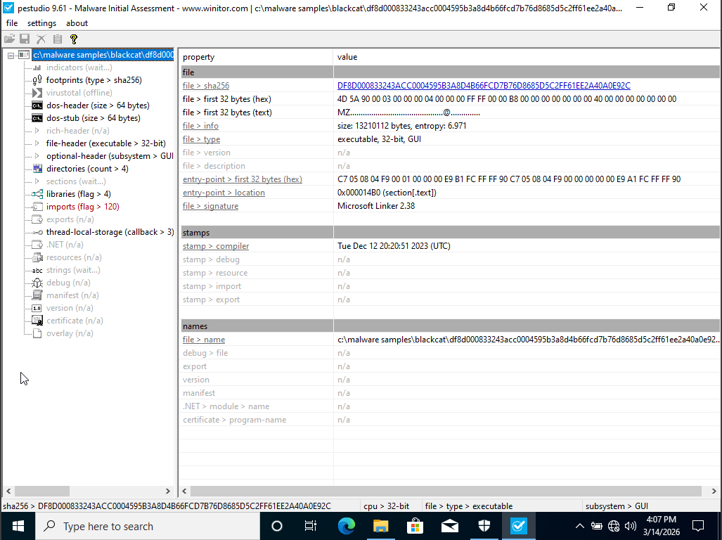
- Performed static analysis with PEStudio to review sample characteristics, metadata, indicators, and suspicious properties before execution.
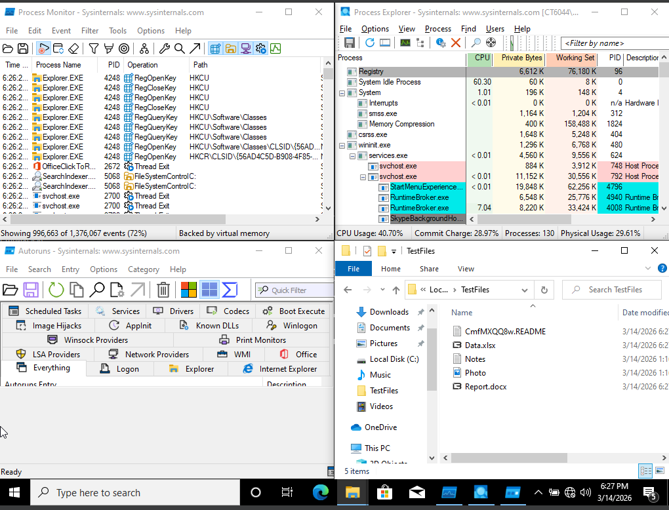
- Performed dynamic analysis with Process Monitor, Process Explorer, Autoruns, and Event Viewer to observe process, file-system, persistence-related, and system behaviour.
- Compared LockBit and BlackCat (ALPHV) behaviour using original investigation evidence, sample hashes, and controlled test files.
Key Findings
- Observed encryption of controlled test files during ransomware execution.
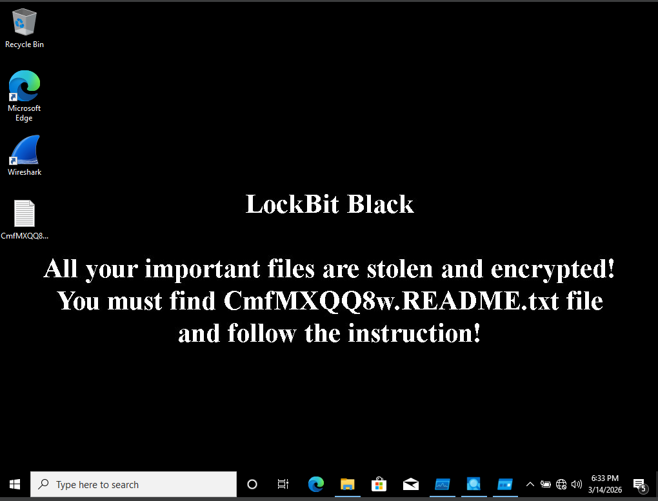
- Observed ransom-note behaviour associated with the analysed ransomware activity.
- LockBit modified the Windows desktop wallpaper as part of its execution behaviour.
- Process and file-system activity provided evidence of runtime ransomware behaviour.
- BlackCat exhibited reconnaissance-related behaviour during the controlled analysis.
- Sample hashes and original investigation evidence were retained to support traceability of the analysis.
Technical Evidence
Selected original investigation evidence from the isolated ransomware-analysis lab. Open an image to inspect it at full size.
Safety & Evidence Boundary
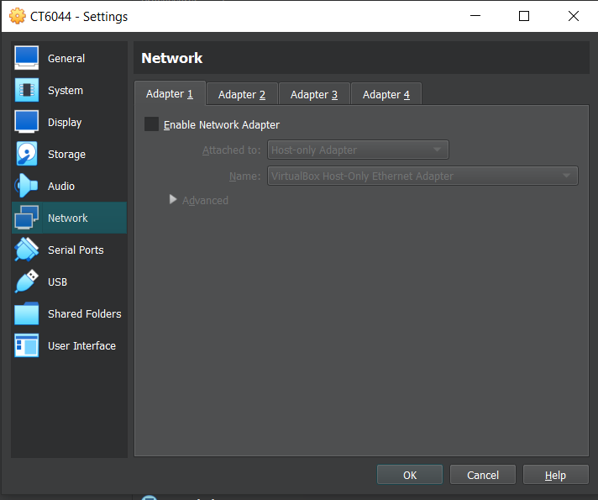
All dynamic analysis was performed inside an isolated laboratory environment using controlled test files. The portfolio documents investigation methodology and evidence only; malware samples are not hosted or distributed through this website.
Security Relevance
The project demonstrates structured malware-analysis methodology, controlled observation of ransomware behaviour, process and file-system investigation, evidence documentation, IOC-oriented thinking, and awareness of containment and incident-response requirements.